ReleasedAug 2026 — present
Dockmaster
Know what's running on your Mac and your homelab.
01The problem
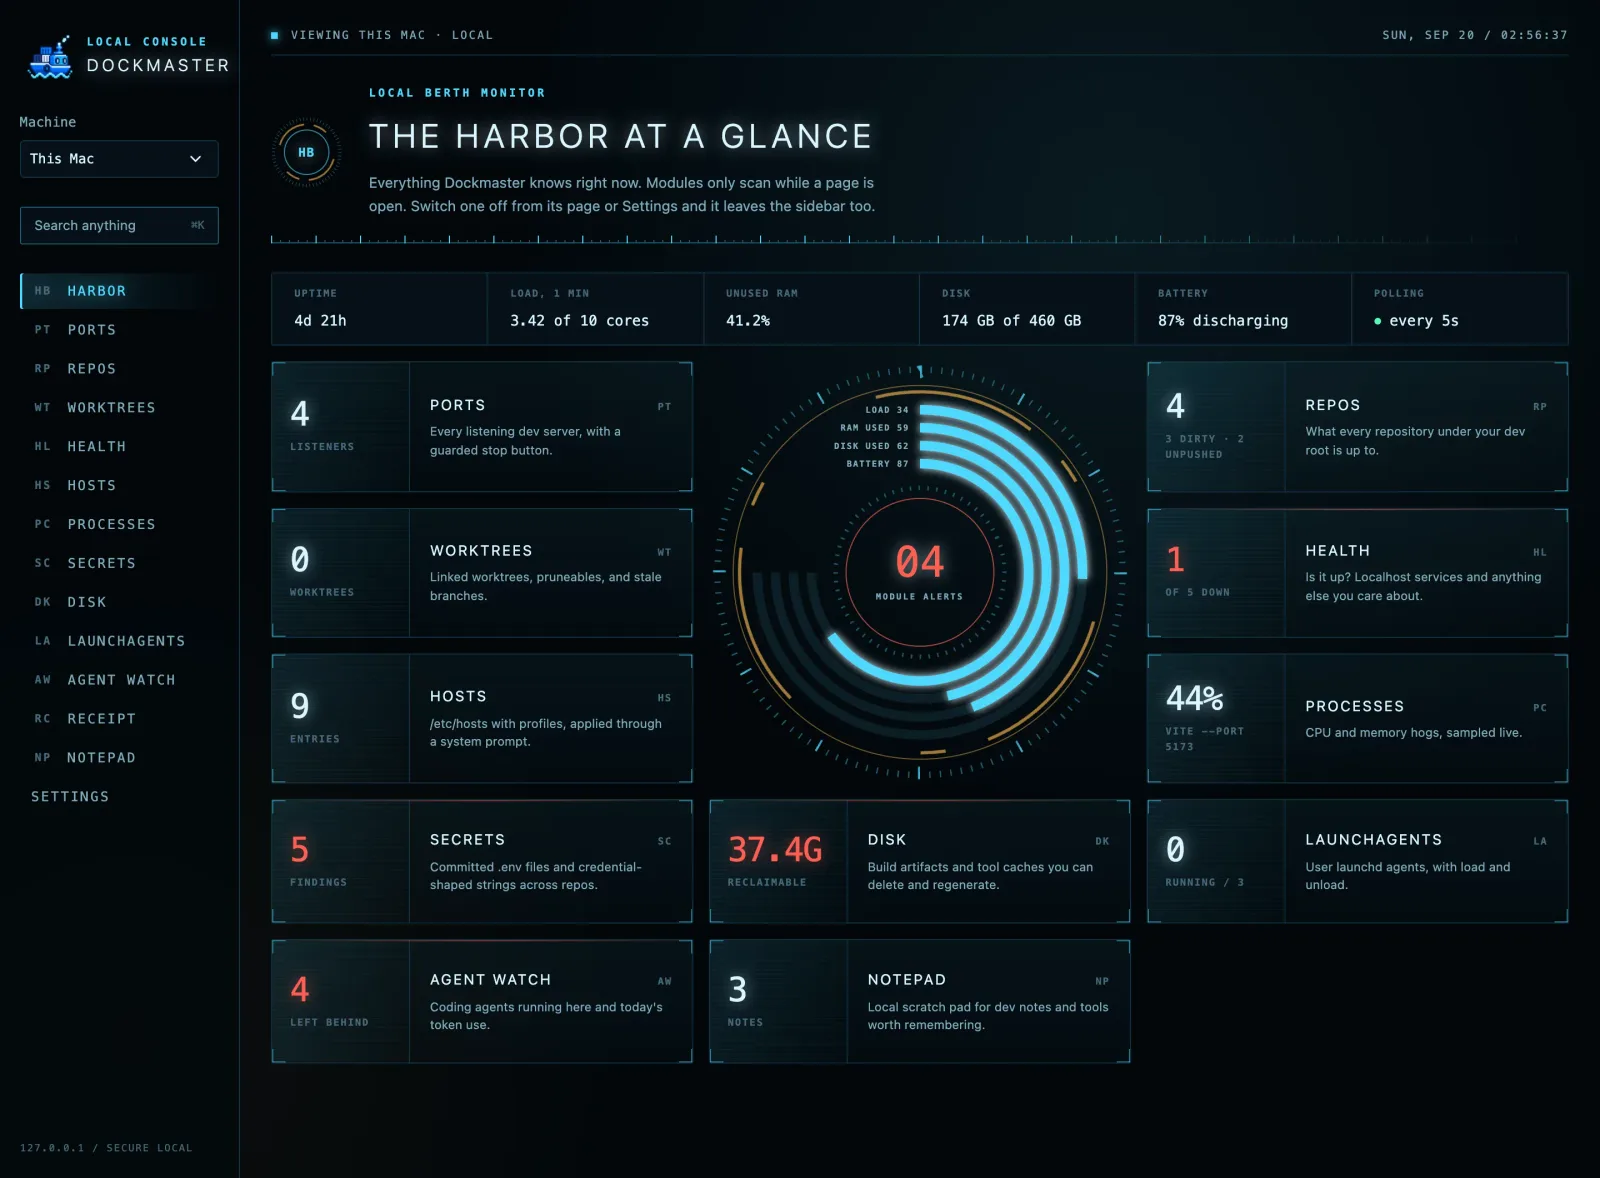
Dev machines fill up with things nobody remembers starting: servers on random ports, worktrees from finished branches, gigabytes of build output, and now coding agents that leave processes behind.
Dockmaster grew out of Port Authority, a single-file port dashboard. The idea scaled: a dev tool should know what's on your machine, and it should be able to act on it safely.
02What I built
01
Ports and Processes
Every listening dev server with a guarded stop: tree-kill, SIGTERM then confirmed SIGKILL, PID-reuse protection and LAN-exposure badges. Never PID 1 or Dockmaster's own ancestors.
02
Repos and Worktrees
A status board for every git repo under your dev root, plus stale worktrees and branches you can prune. Main worktrees and default branches are off limits.
03
Agent Watch
Coding agents running right now (Claude Code, Codex, OpenCode, Gemini CLI and more) with the repo each is in, seven days of sessions, and the servers they left behind, with a cleanup that re-scans and refuses while an agent is still in the folder.
04
Secrets and Disk
Credential-shaped strings in tracked files, redacted server-side so the API never returns full secret text. Reclaimable space from node_modules, build output and tool caches, deleting only exact artifact names.
05
Receipt
The last seven days as a shareable receipt: sessions per agent, tokens, lines changed, cost, and what Dockmaster stopped, removed and reclaimed.
06
Remote Macs
Works on a homelab over your own SSH. Nothing leaves your machines.
03Architecture
A Next.js app you run on loopback. Each module shells out to the tool that already knows the answer (lsof, ps, git, du, launchctl, the Docker daemon) and every destructive action re-verifies its target right before acting.
Every scanning module can be switched off, and settings, notes and the action log live in ~/.dockmaster as plain JSON.
04Screens
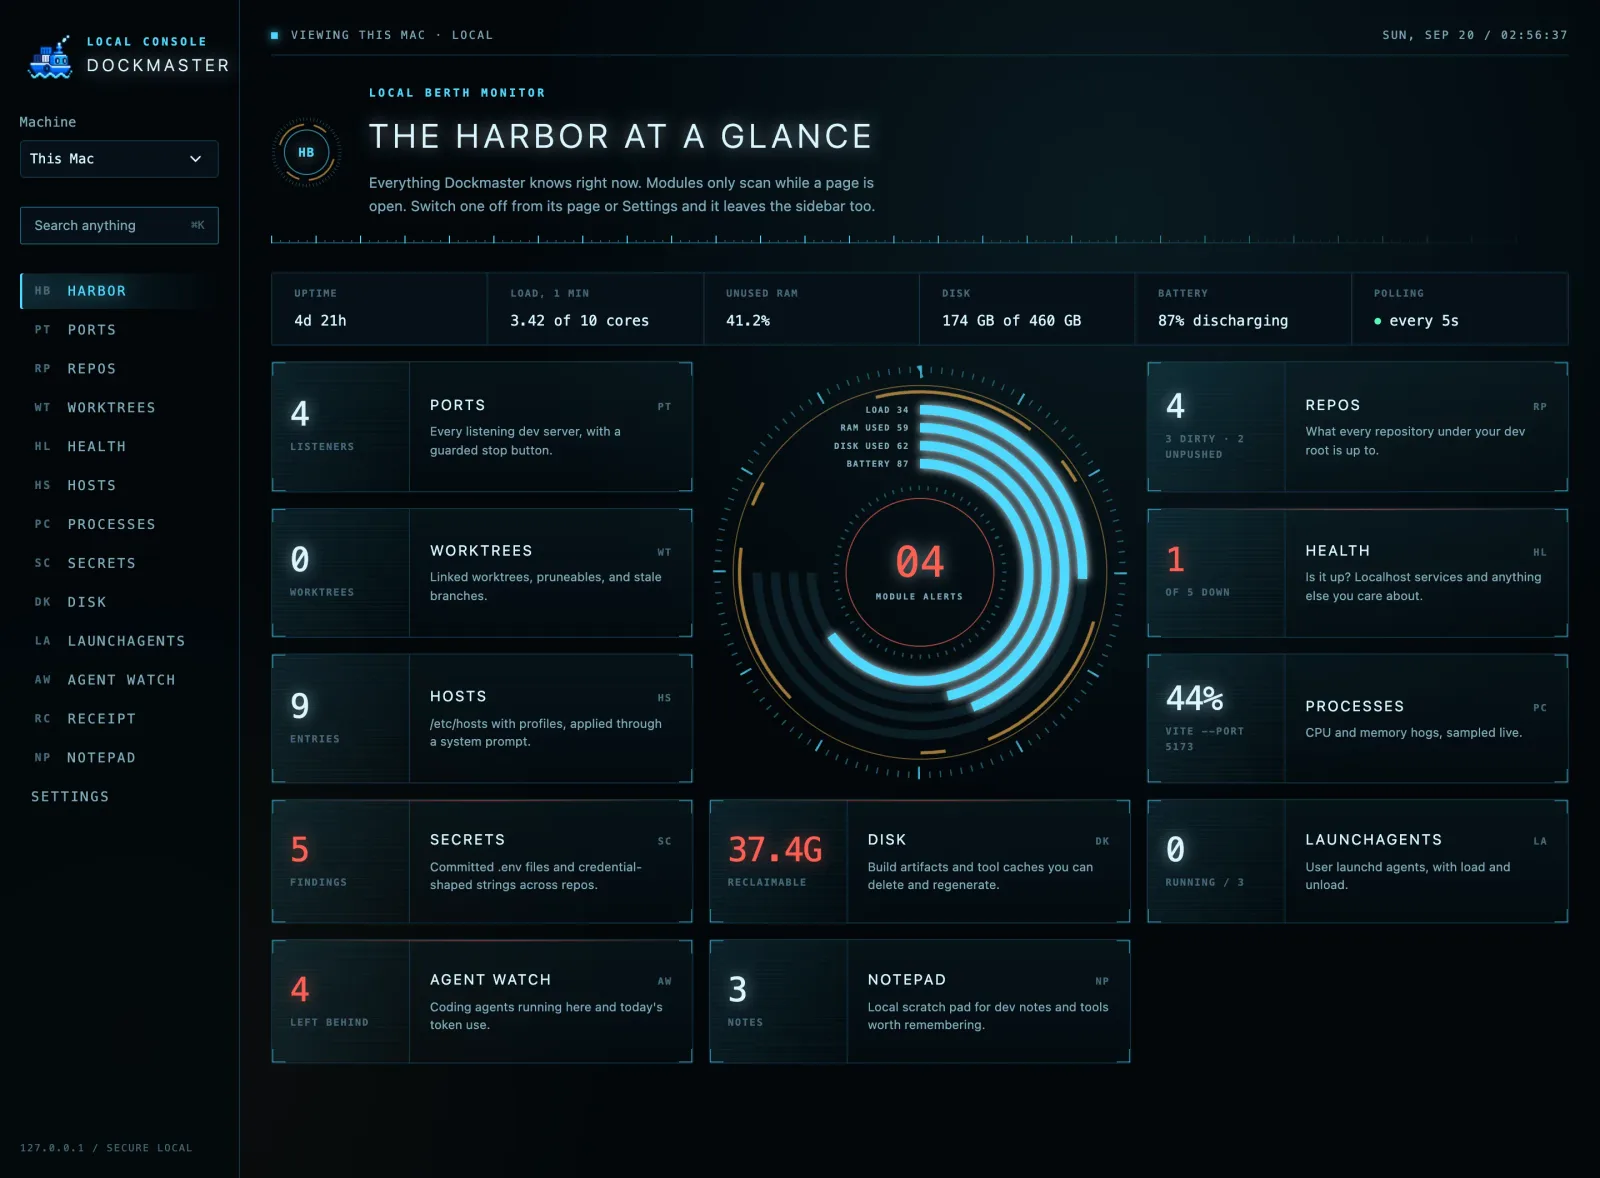
Harbor: one live card per module plus system vitals 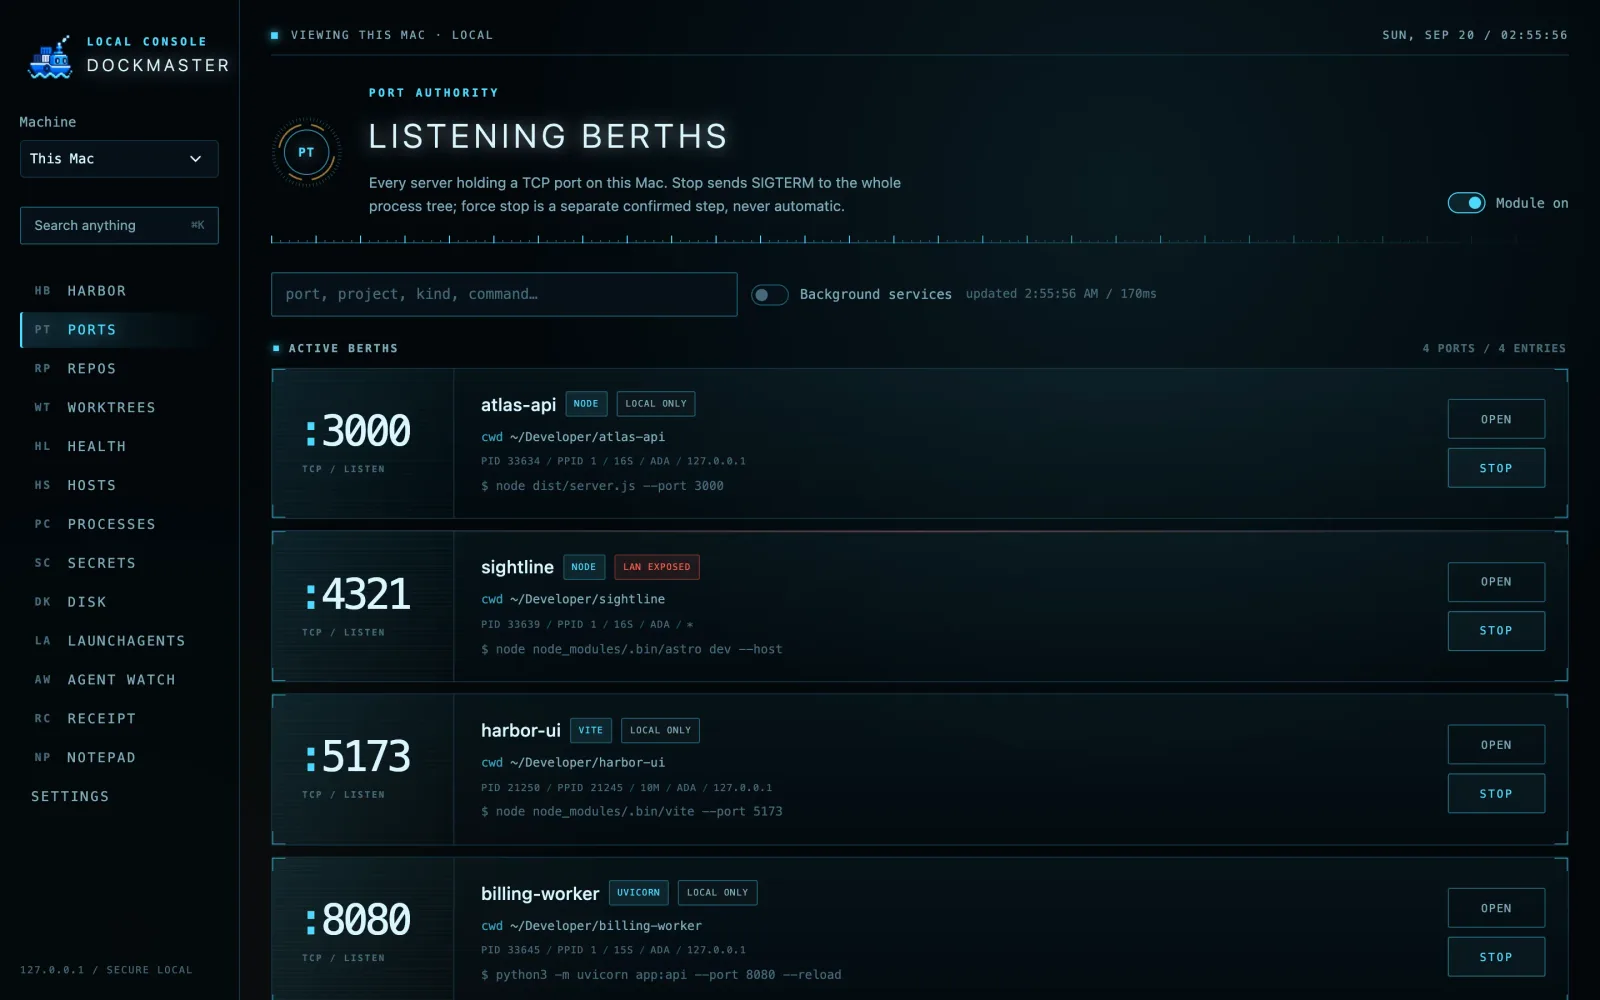
Ports: every listening dev server, with a guarded stop 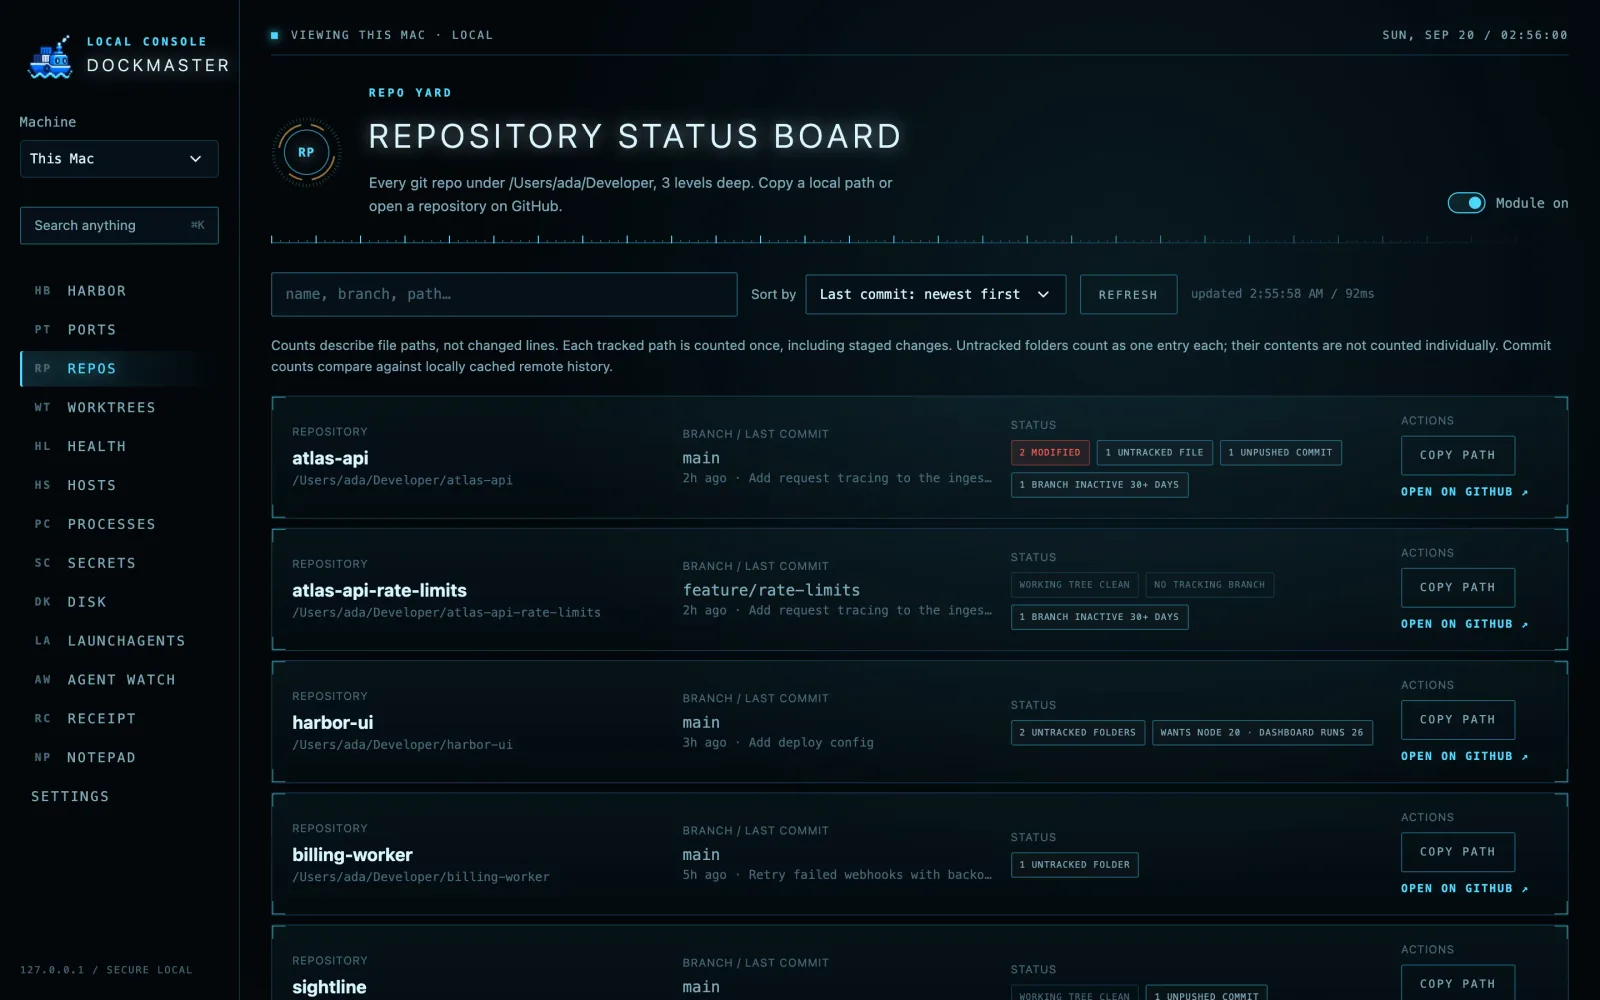
Repos: dirty files, ahead/behind and stale branches under your dev root 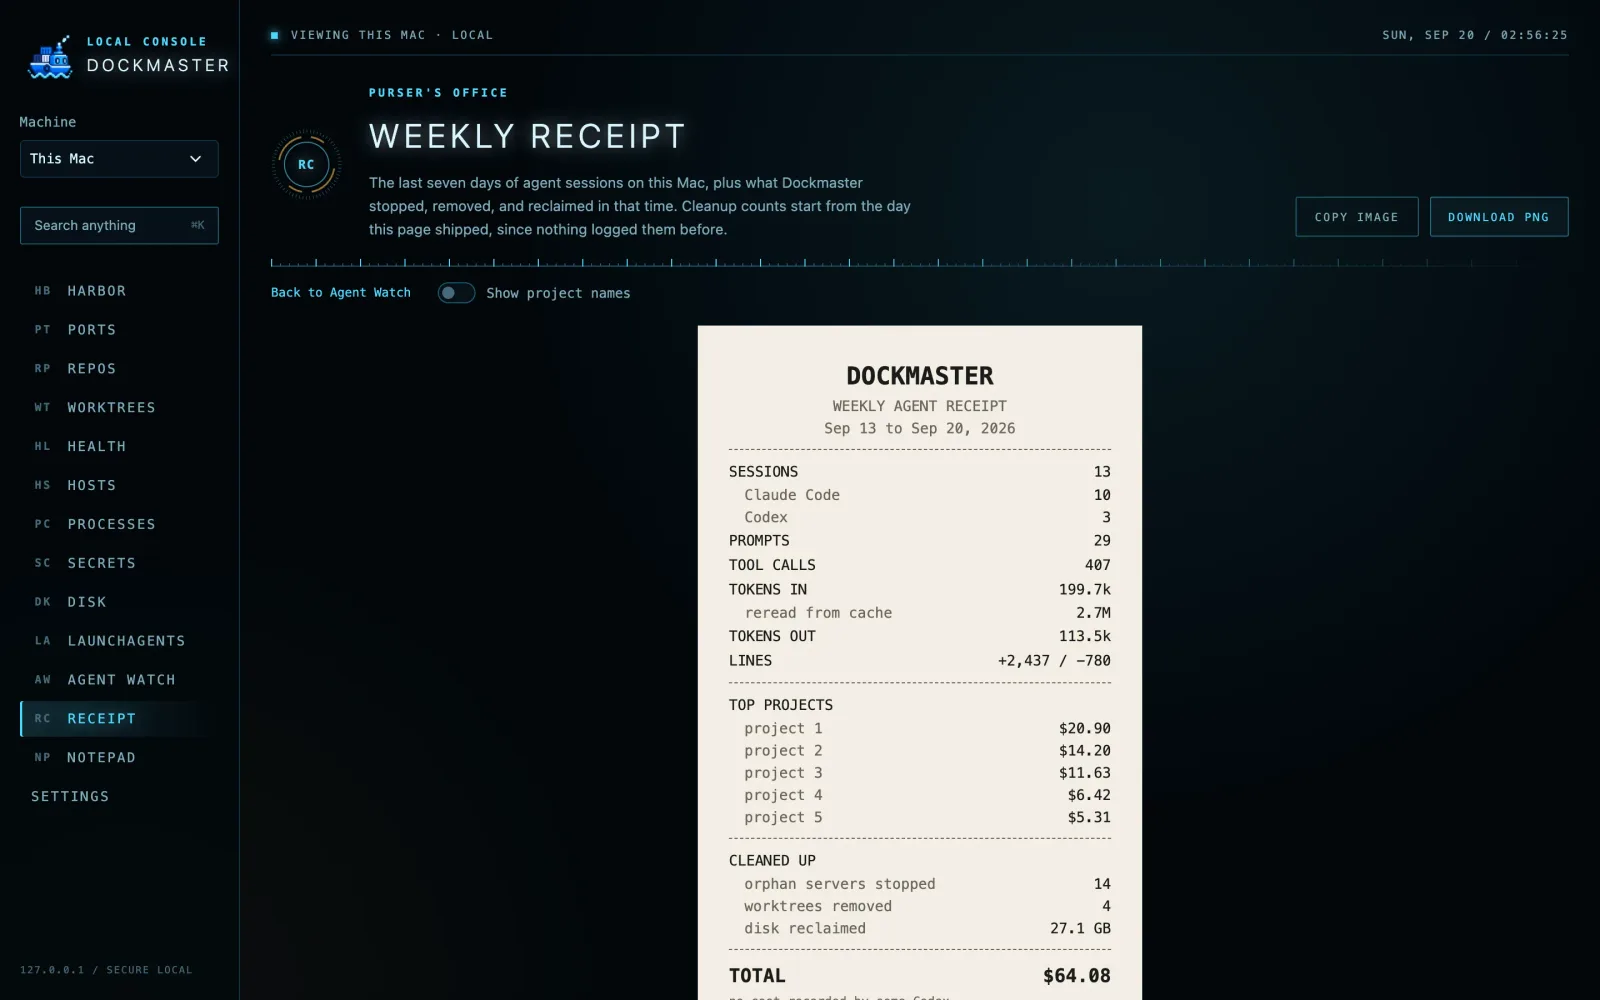
Receipt: the last seven days of agent work as a shareable image